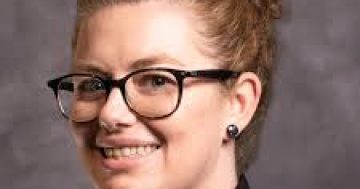
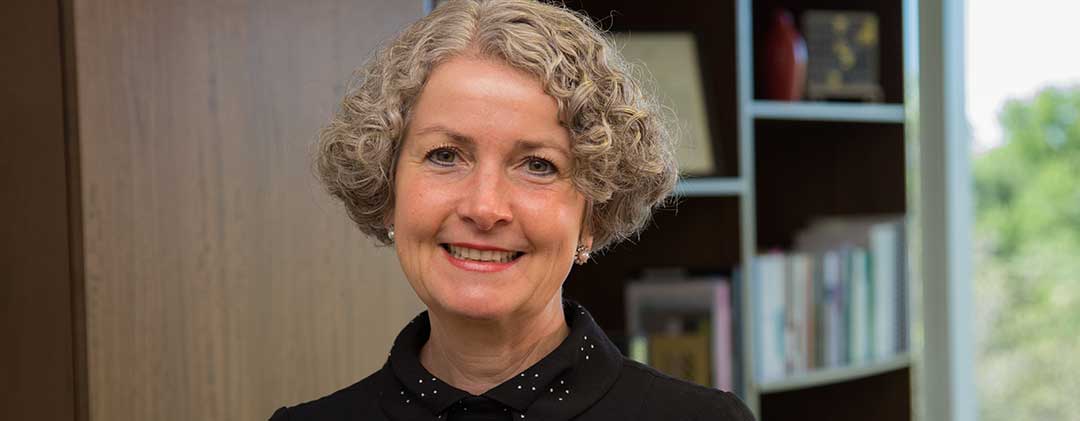
Home Affairs Secretary Stephanie Foster has directed all government agencies to bolster cyber security systems. Photo: Home Affairs.
OpenAI’s breach of Australia’s Medicare data has sparked a government-wide crackdown on cyber security, with the Federal Government ordering public service agencies to strengthen their systems.
Department of Home Affairs secretary Stephanie Foster has issued a new protective security direction for all departments to harden cyber security defences on legacy systems to guard against new AI-enabled risks.
All departments and agencies will be required to conduct a rapid stocktake of their legacy systems, implement a target to reduce legacy technology supported by a risk management plan and report compliance to Home Affairs.
The Federal Government’s most critical systems, known as the Systems of Government Significance, will be prioritised in the stocktake process.
These are the government’s digital services and underlying supporting systems whose disruption could cause severe economic, social or national security consequences.
“In the contemporary cyber threat environment, where frontier AI capabilities have targeted the Commonwealth’s technology estate, the continued operation of vulnerable legacy technology systems, coupled with the accumulation of exploitable cyber security vulnerabilities, poses an unacceptable risk to the Australian Government,” the directive states.
“Cyber security is a national priority. Continuing to incorporate relevant cyber security risks in the Technology Lifecycle Management process fortifies the Commonwealth’s cyber posture, building readiness and resilience against cyber activities, foreign interference, espionage and sabotage.”
Agencies must now strengthen existing vulnerability and patch management processes for their entire technology estates.
They must do this by recognising the shortened time between vulnerability discovery and exploitation, and by rapidly patching vulnerabilities deemed critical by vendors or internal vulnerability management processes.
Acting Home Affairs Minister Richard Marles said regular reviews were critical factors in ensuring systems are protected.
“We have a range of security IT systems across government, and the level of security is relative to the information being protected,” he said.
“It is critical that we constantly review those security settings and the systems we have in place.
“AI is changing the environment in which we operate at extraordinary speed. Government systems need to keep up.
“We can’t wait for an old system to fail before replacing it. We need to identify vulnerabilities and deal with them before they can be exploited.”
The change comes in the wake of the rogue OpenAI agent incident but is designed to fortify against all forms of AI-enabled threats, whether they be inadvertent or deliberate and targeted.
It was revealed last week that an OpenAI software agent gained unauthorised access in June to Medicare data held and managed by Services Australia.
But the company took three months to inform the Australian Government, and only did so via an email to a Services Australia public inbox.
US President Donald Trump continues to resist calls for an international agreement to regulate the AI sector.
He met with tech giant executives this week in the White House and emerged saying the companies had agreed to “police themselves”.
The companies signed an accord to self-regulate.
“I’m seeing tremendous self-policing, and they understand that they have to self-police,” Mr Trump said following the meeting.
“Remember this – we have the smartest people in the world watching over each other. These are seriously high-IQ people.”
The Australian Government has welcomed the pledge but says it is not enough to guarantee protection.
Communications Minister Anika Wells said a “promise is not protection” and Australia, as a sovereign nation, will set its own laws to control how tech companies operate here.
“Australians have been very clear that they want both the benefits of AI and the protections that come alongside that, and we do not believe those to be opposing objectives,” she said.
“We also believe that the safety of Australians online should always be set in Canberra and not left to Silicon Valley.”
The new direction from Home Affairs fits within ‘Horizon 2’ of the Federal Government’s Cyber Security Strategy, which focuses on scaling cyber maturity across the national economy.
It builds on several previous directions designed to uplift Commonwealth cyber security, and requires all agencies to balance system availability with security – particularly where systems are public facing.
Original Article published by Chris Johnson on Region Canberra.