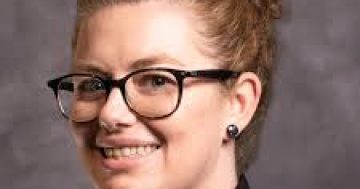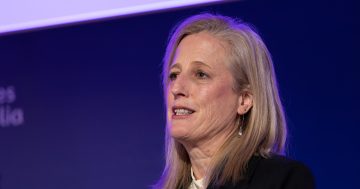

Narelle Devine will head the government’s Cyber Incident Review Board. Photo: Narelle Devine.
A new Cyber Incident Review Board has been established to review hacking security breaches in the public and private sectors.
It is an independent statutory advisory body charged with conducting no-fault post-incident reviews of significant cybersecurity incidents in Australia.
The board will make actionable recommendations to the Federal Government and to industry after each significant incident.
Those recommendations will outline actions to prevent, detect, respond to, or minimise the impact of similar cybersecurity incidents in the future.
Cyber Security Minister Tony Burke said the government established the board to ensure Australia is best placed to learn key lessons from cyber incidents and improve national resilience to them.
“We know that cyber attacks are constant. This guarantees we learn from every attack and keep increasing our resilience,” the minister said.
“The Cyber Incident Review Board will examine major cybersecurity events, develop findings, and provide recommendations to improve national cyber resilience across government and industry.”
The board is established under the Cyber Security Act 2024 and is a component of the Federal Government’s 2023-2030 Australian Cyber Security Strategy.
It supports efforts to make Australia one of the world’s most cyber-secure nations by 2030, with resilient, cyber-ready communities, strong businesses and a secure national economy.
Telstra’s global chief information security officer, Narelle Devine, has been appointed as the inaugural chair of the seven-member board.
Mr Burke said together, the appointed members bring deep cyber security expertise, alongside strong technical, governance, legal, national security, and community experience, ensuring the board is well placed to provide trusted, independent advice to government and industry.
“Australia is fortunate to have highly experienced cybersecurity leaders guiding this work,” he said.
“These appointments reflect our collective commitment to keeping Australians safe in an increasingly complex cyber environment.”
The Cyber Incident Review Board appointments are:
- Ms Narelle Devine (Chair), Global Chief Information Security Officer, Telstra
- Professor Debi Ashenden, Director of the Institute for Cyber Security, University of New South Wales
- Ms Valeska Bloch, Partner and Head of Cyber, Allens
- Mrs Jessica Burleigh, Chief Information Security Officer, Boeing Australia
- Mr Darren Kane, Chief Security Officer, NBN Co
- Mr Berin Lautenbach, Global Head of Information Security, Toll Group
- Mr Nathan Morelli, Head of Cyber Security and IT Resilience, SA Power Networks.
The board will only review an incident after it has occurred and initial investigation and response efforts have been completed.
Its reviews will then focus on a single incident or a group of similar incidents and may highlight features such as the attack method, the type of system affected, or a known vulnerability.
It will not assign blame or determine who is responsible for an incident, and published reviews will not include personal or classified information, including anything that could affect national security, defence, or international relations of the Commonwealth.
Explaining on its website the role and need for the board, the Department of Home Affairs states that recent cyber-attacks have shown that “government and industry need to learn more from these events”.
“The board reviews will identify the contributing factors to cyber incidents to help sectors prepare for future cyber attacks,” it states.
The Cyber Security Act 2024 establishes the board as an independent advisory body. An expert panel will also be drawn from a pool of industry sector experts to support the board.
Original Article published by Chris Johnson on Region Canberra.